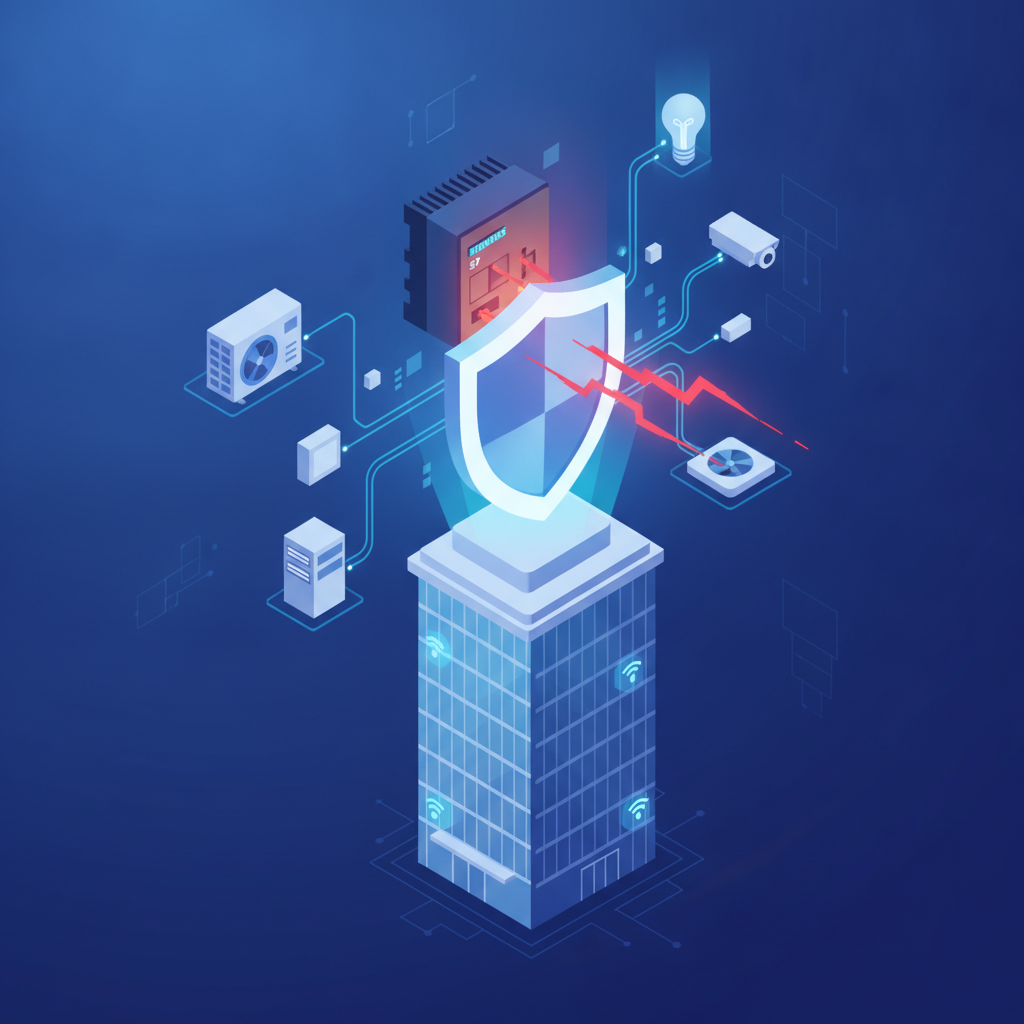
A high-stakes joint cybersecurity advisory from the NSA, CISA, FBI, DOE, and EPA has issued a stark warning to owners and operators of industrial control systems (ICS). There is an active, targeted cyber threat currently exploiting Siemens S7 Series programmable logic controllers (PLCs). However, this is not merely a Siemens-specific vulnerability—it is an industry-wide escalation.
While the advisory explicitly highlights the Siemens S7 family, the authoring agencies stress that ongoing PLC targeting activity spans across multiple hardware vendors. For building automation architects and facility managers, this serves as a critical reminder that operational technology (OT) networks are squarely in the crosshairs of advanced threat actors.
The Reality of Cyber-Physical Threats in Smart Buildings
PLCs and BACnet controllers act as the central nervous system of our smart buildings and industrial facilities. They control everything from complex HVAC chiller plants to lighting grids and life-safety systems. When a threat actor compromises a PLC, they gain the ability to manipulate physical environments directly.
The implications for commercial real estate and industrial facilities are severe. Unauthorized access to a PLC’s ladder logic can lead to manipulated temperature setpoints, forced equipment shutdowns, or bypassed safety overrides. This is no longer a theoretical risk; it is an active exploitation campaign.
The Danger of Internet-Exposed Infrastructure
One of the most glaring vulnerabilities in legacy building automation is the exposure of PLCs directly to the public internet. Historically, system integrators have exposed ports to simplify remote troubleshooting and maintenance. In today’s threat landscape, this practice is a critical liability.
The federal advisory lists removing internet access to PLCs as a top mitigation priority. Threat actors actively scan public IP ranges for exposed ICS protocols. If your building’s automation network is visible on platforms like Shodan, it is only a matter of time before it is targeted.
Essential Defense and Mitigation Strategies
Securing a building’s OT network requires a defense-in-depth approach. The federal agencies mandate several immediate actions for facility managers to reduce the attack surface and hunt for potential compromises.
Asset Visibility and Patch Management
You cannot protect what you cannot see. Operators must immediately inventory all programmable logic controllers across their portfolios. Once identified, administrators must apply critical security patches and strengthen network access controls to ensure only authorized engineering workstations can communicate with the devices.
Anomaly Hunting and Network Hardening
Defenders must actively monitor for unauthorized activity and harden PLC services. This includes verifying ladder logic integrity to ensure that the controller’s core programming hasn’t been maliciously altered. Implementing continuous telemetry monitoring is essential for identifying anomalies before they result in physical system failure.
Modernizing OT Security with Cloud-Native Architecture
The challenge for modern facility operators is balancing the need for remote accessibility with the stringent security requirements of industrial control systems. Exposing PLCs is no longer an option, but operators still need real-time data and remote control to optimize energy and maintenance.
This is where specialized platforms like BAaaS.io bridge the gap. By utilizing a Building Automation as a Service architecture, properties can achieve secure, centralized control without exposing edge devices to the public web. The platform creates an integrated building information sphere that acts as a secure buffer between the hardware and the operator.
Furthermore, BAaaS.io provides robust access control and role-based authentication, ensuring that only verified personnel can execute automated environmental adjustments or view real-time telemetry. This inherently satisfies CISA’s recommendations for strengthened access controls and proactive monitoring.
Conclusion
The joint advisory regarding the Siemens S7 Series PLCs is a massive wake-up call for the building automation industry. As threat actors pivot from IT data theft to OT physical disruption, the security of our building infrastructure must evolve.
Facility managers must act immediately to audit their networks, eliminate internet-facing controllers, and adopt secure, centralized management platforms. By treating OT cybersecurity as a core component of building operations, we can protect our occupants, preserve equipment lifecycles, and ensure uninterrupted operations in an increasingly hostile digital landscape.