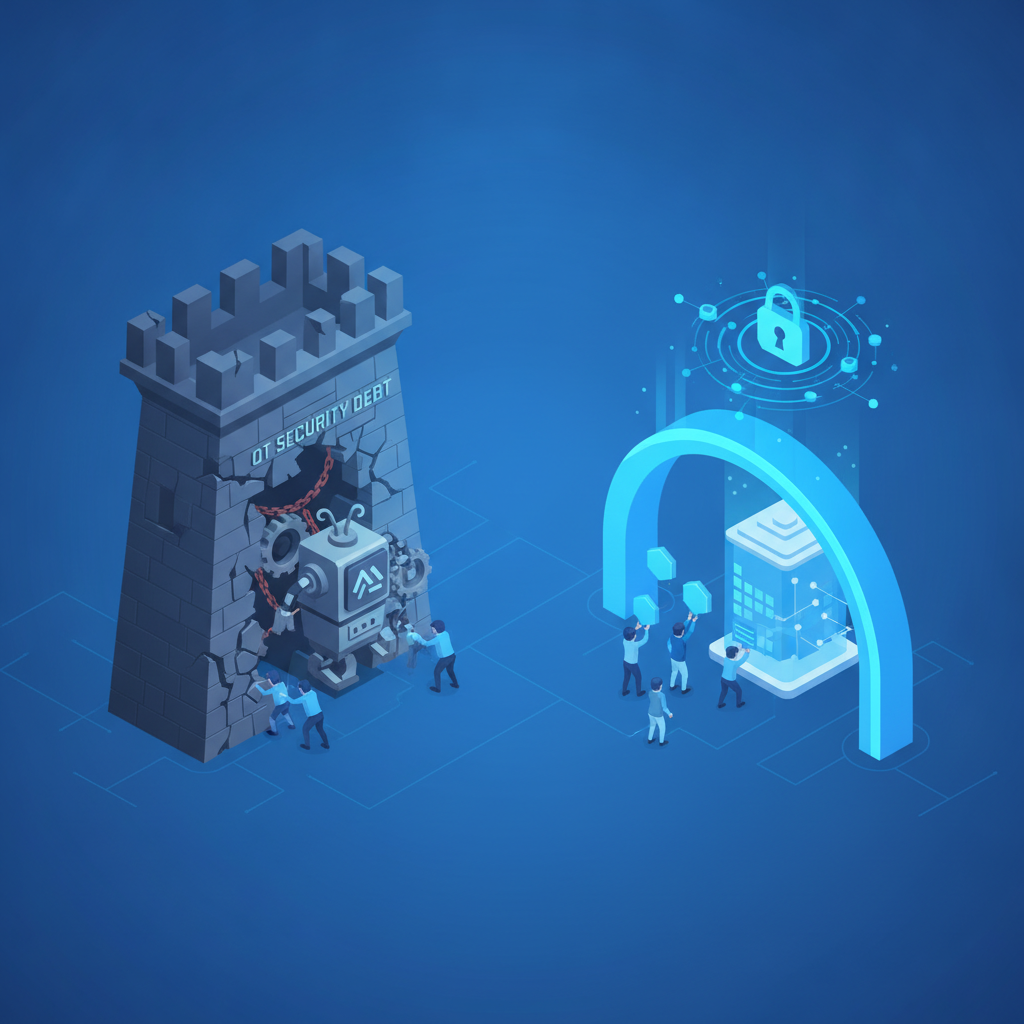
For over two decades, the rush to modernize operational technology (OT) has created a compounding, often invisible crisis. As facilities pushed for deeper IT/OT convergence, enterprise connectivity, and advanced analytics, they inadvertently accumulated massive “security debt.” This debt wasn’t born of negligence, but of pragmatic, incremental decisions made by engineers trying to keep legacy systems functional in an increasingly connected world.
Today, the consequences of disconnected modernization are stark. Critical infrastructure, smart buildings, and manufacturing plants are riddled with architectural mismatches. New cloud technologies have been stacked on top of aging PLCs and outdated protocols without any structural redesign for security. The result is a highly connected, highly vulnerable environment where a single compromised credential can expose an entire operational network.
The Anatomy of Compound Security Exposure
Between 2000 and 2020, organizations aggressively added capabilities to their legacy OT systems. Previously air-gapped environments were suddenly linked to enterprise resource planning (ERP) systems, vendor remote access tools, and cloud platforms. However, these connections were typically engineered for availability, not zero-trust security.
The most devastating architectural flaw introduced during this era was the creation of large, flat OT networks. When control systems, safety instrumented systems, HVAC controllers, and modern IoT sensors share a single broadcast domain, the blast radius of any cyber incident expands exponentially. In these environments, an attacker doesn’t need to execute complex lateral movement; a single foothold provides unchecked access to the entire environment.
Furthermore, remote access tools like VNC or RDP were frequently deployed using shared credentials and default administrator accounts. While these shortcuts allowed technicians to troubleshoot systems quickly, they also eliminated the need for threat actors to hunt for privilege escalation, turning minor breaches into catastrophic operational failures.
The Modbus Dilemma in Modern ICS Security
At the heart of this security debt lies the continued reliance on legacy protocols like Modbus and Profibus. These protocols remain the backbone of industrial control and building automation systems worldwide. However, they were designed for completely isolated, trusted environments. They inherently lack basic security controls such as authentication, encryption, and data integrity verification.
Because you cannot retrofit encryption into a native Modbus transmission without breaking compatibility, the solution must be architectural rather than protocol-level. Modbus traffic should never cross the Purdue Model Level 2 perimeter in its native form. Any data required by enterprise users or cloud analytics should be handled through secure intermediaries, such as a historian, a proxy, or an industrial firewall located in a well-defined Demilitarized Zone (DMZ).
Organizations must adopt a defense-in-depth strategy around these protocols. By enforcing strict IT/OT segmentation and blocking unexpected write commands at the firewall level, operators can maintain the utility of their legacy equipment while neutralizing the risk of unauthorized external manipulation.
Architectural Flaws vs. Incremental Debt
Identifying security debt requires understanding the difference between a missing security control and a fundamentally broken architecture. Incremental debt involves issues like missing patches, weak passwords, or unmonitored workstations. These risks can usually be mitigated over time through system hardening, scheduled maintenance windows, and compensating controls without requiring a total system overhaul.
Architectural debt, on the other hand, demands structural intervention. If a facility relies on a flat network where business IT and safety systems share infrastructure, or if a site uses undocumented communication pathways that bypass security perimeters, incremental fixes will fail. In these brownfield scenarios, adding another firewall won’t solve the underlying risk; significant investment in network segmentation and system redesign is required.
The clearest indicator of an organization’s maturity is how it quantifies these risks. Leaders in ICS security use OT Cyber Risk Quantification (CRQ) to translate technical vulnerabilities into financial baselines, allowing boards to prioritize remediation based on potential downtime, physical damage, and safety implications rather than just CVSS scores.
A Strategic 3-Year Remediation Blueprint
Eradicating decades of security debt cannot happen overnight, especially in brownfield environments constrained by stringent production schedules. A successful turnaround requires a phased, risk-based approach.
Year 1: Visibility and Containment
The immediate priority is discovering exactly what exists on the network. Organizations must build a comprehensive asset inventory, map all critical connections, and lock down remote access pathways. By identifying the “crown jewels” and addressing obvious segmentation gaps, teams can quickly establish containment boundaries around the highest-risk legacy systems.
Year 2: Deep Segmentation and Monitoring
With visibility established, the focus shifts to enforcing strict network zones and conduits. This involves isolating critical DCS, PLC, and safety networks from general operational traffic. This is also the stage to implement continuous monitoring, strict vulnerability management, and robust access controls to detect anomalous behavior.
Year 3: Lifecycle Management and Replacement
In the final phase, organizations must confront their unsupported, end-of-life systems. The highest-risk assets that cannot be secured through compensating controls must be replaced. Furthermore, incident response plans must be rigorously tested through tabletop exercises to ensure defenses operate exactly as intended.
Modernizing Building Automation Securely
While industrial plants face significant hurdles, the commercial real estate sector is dealing with identical challenges in building automation. As HVAC, lighting, and physical security systems converge onto standard IP networks, facility managers are exposed to the same flat-network vulnerabilities that plague manufacturing.
Managing this complex lifecycle securely requires a specialized, cloud-managed ecosystem. This is where BAaaS.io provides a vital solution. By offering Building Automation as a Service, the platform delivers centralized control and real-time telemetry while enforcing strict, role-based access control. It bridges the gap between legacy infrastructure and modern analytics, ensuring that smart buildings achieve maximum energy efficiency and occupant comfort without compromising their underlying security architecture.
Conclusion
The OT security crisis is not an insurmountable technical failure; it is a debt management problem. Organizations that successfully navigate this challenge do not attempt to rip and replace their entire operational infrastructure. Instead, they distinguish between acceptable risks and architectural flaws, applying targeted controls to contain legacy protocols.
By transforming unmanaged exposure into conscious, quantified risk management, industrial and facility leaders can modernize their environments safely. The key is ensuring that the rate of debt reduction outpaces the speed at which new technological complexities are introduced.